Me

Principal DevSecOps Engineer

Jason Ziemba

Kubernetes, GitOps & Infrastructure-as-Code Specialist

Exploring My Next Opportunity Active Top Secret Clearance Cumming, GA 15+ Years Experience

I build and run secure, automated, cloud-native infrastructure — turning legacy systems into resilient Kubernetes and GitOps platforms across federal and enterprise environments.

About

I'm a Principal DevSecOps/SRE engineer with 15+ years automating secure, scalable Kubernetes, GitOps, and Infrastructure-as-Code platforms across federal and enterprise environments. I specialize in modernizing legacy systems into resilient, cloud-native infrastructure — improving reliability and operational efficiency along the way. Outside of my day job, I run a production-grade home lab that mirrors the same enterprise-scale platform engineering practices I bring to client and employer work.

  • Experience15+ yrs professional, 25+ yrs hands-on
  • CertificationSecurity+ (CompTIA), Aug 2023 (exp. Aug 2029)
  • ClearanceActive Top Secret
  • EducationNo formal degree — hands-on systems engineering & DevOps experience

My Journey

My path into this field started with a Commodore 64 — chasing programs about authentication, encryption, and system security long before I understood why that stuck with me. Perl carried me through high school and into my first job automating an AS/400 for my local school district, then webmastering a second district where I learned Linux, early VMware (back when it was GSX/ESX), and PHP by building a self-service platform that let schools spin up their own sites — DNS, storage, and plugins included.

Moving to Georgia in 2004 for a NOC role at CNN, I started a home lab that's been rebuilt and re-architected more times than I can count — chasing whatever the industry was actually doing at the time. Bare-metal boxes gave way to virtualized hosts, then containers, then a proper Kubernetes cluster; manual changes gave way to GitOps; and more recently, self-hosted AI has joined the stack, with local and cloud models routed through agents that help me catch things I'd otherwise miss. The specifics keep changing (see the current platform below); what hasn't is the habit of learning a technology by actually running it.

Outside of the keyboard, I dabble with my 3D printers and laser system — different kind of building, same itch.

Skills

Platforms & Orchestration

  • Kubernetes
  • Rancher RKE2
  • AWS EKS
  • Docker
  • Helm
  • Istio
  • Argo CD
  • Harbor

IaC & Configuration Management

  • Terraform
  • Chef
  • SaltStack
  • Git

CI/CD

  • GitLab CI/CD
  • Gitea Actions

Languages

  • Perl
  • Go
  • Python
  • PHP

Observability

  • Prometheus
  • Grafana

Security & Compliance

  • AWS Security Hub
  • Wazuh (SIEM)
  • STIG/CVE Remediation
  • ATO Compliance Support

Data & Deployment

  • Talend (ETL)
  • ETL Frameworks
  • Blue/Green Deployments

Experience

RAFT — Principal DevSecOps Engineer

Remote · December 2022 – Present

Continuation of the same federal platform program following a change in prime contractor

  • Manage Rancher-based Kubernetes clusters using CI/CD pipelines and Infrastructure as Code (Terraform + GitLab), automating provisioning and updates across federal cloud environments and eliminating manual configuration drift.
  • Delivered production Kubernetes platform automation across four architecture iterations — including migrating and consolidating from ~80 RKE2 clusters to a streamlined 10–15 EKS cluster footprint — adapting to evolving mission requirements.
  • Deployed and maintain BigBang (Platform One) to provide streamlined package deployment and updates across 10+ Kubernetes clusters.
  • Monitor AWS Security Hub for STIG and CVE compliance findings across AMI builds and cluster workloads; remediate through configuration and image-build adjustments to maintain ATO posture.
Omni Federal — Senior DevOps Engineer

Remote · July 2021 – December 2022

  • Enhanced multiple Kubernetes operators written in Go, reducing manual intervention and improving operational reliability for platform users.
  • Optimized automated deployment processes on Rancher-managed Kubernetes clusters running on Docker, integrating with GitLab CI/CD pipelines.
  • Developed a Helm chart processing pipeline generating artifact checklists, enabling consistent, repeatable air-gapped deployments.

E*Trade / Morgan Stanley — Principal System Engineer

Alpharetta, GA · July 2019 – July 2021

  • Converted legacy scripts into containerized Docker images, improving portability across oVirt and VMware virtualization environments.
  • Rewrote legacy Perl scripts, cutting runtime from over an hour to under 5 minutes.
  • Developed Perl and Python scripts, scheduled via cron, to aggregate Prometheus monitoring data, establish baselines, and detect anomalous behavior.

Healthgrades / RVO Health — ETL/Data Consultant

Atlanta, GA · July 2019 – July 2024 (concurrent with full-time roles)

  • Designed and built a custom ETL framework that automatically detected schemas from emailed reports, validated against database schemas, and suggested improvements prior to ingestion.
  • Developed one-off Talend jobs for data aggregation and comparison exercises.
  • Developed custom web UIs and forms for internal data management.
  • Reverse-engineered vendor web systems lacking APIs to enable automated data acquisition and processing.

Earlier Experience

  • Cardlytics — Senior Site Reliability Engineer (Atlanta, GA · Jul 2017 – Jul 2019)
  • The Weather Company, an IBM Business — Senior Cloud Application Engineer (Atlanta, GA · Mar 2014 – Jul 2017)
  • The Weather Channel — Senior Application Engineer (Atlanta, GA · May 2007 – Mar 2014)

Full detail for every role, including these, is available on my complete resume.

Personal Infrastructure Platform

Ongoing personal project, 2015–Present

I run a production-grade home lab that replicates enterprise-scale GitOps and platform engineering practices — end-to-end ownership of Kubernetes, Infrastructure-as-Code, identity, and self-hosted AI infrastructure across 80+ self-hosted services. Everything below is built, automated, and operated the same way I'd run it in a professional environment.

  • Proxmox virtualization platform hosting identity, management, database, and supporting infrastructure services.
  • GitOps software delivery pipeline using Gitea, Harbor, Argo CD, and Kustomize — automating container builds, image publishing, Infrastructure-as-Code, and production deployments.
  • 3-node bare-metal Kubernetes cluster using Istio for ingress and service networking, with Longhorn and NFS for persistent storage, managed declaratively through Git via Argo CD.
  • Portainer managing a separate two-node Docker environment — a lighter-weight container stack alongside the Kubernetes cluster for development work and specialized workloads.
  • Self-hosted AI stack — Ollama, LiteLLM, ComfyUI, OpenWebUI, Hermes, and Hindsight — providing local LLM inference, unified model routing, autonomous agent capabilities, and persistent long-term memory for automation and development workflows.
  • Authentik as a centralized identity provider, implementing OIDC-based SSO across internally hosted applications and reverse proxy infrastructure.
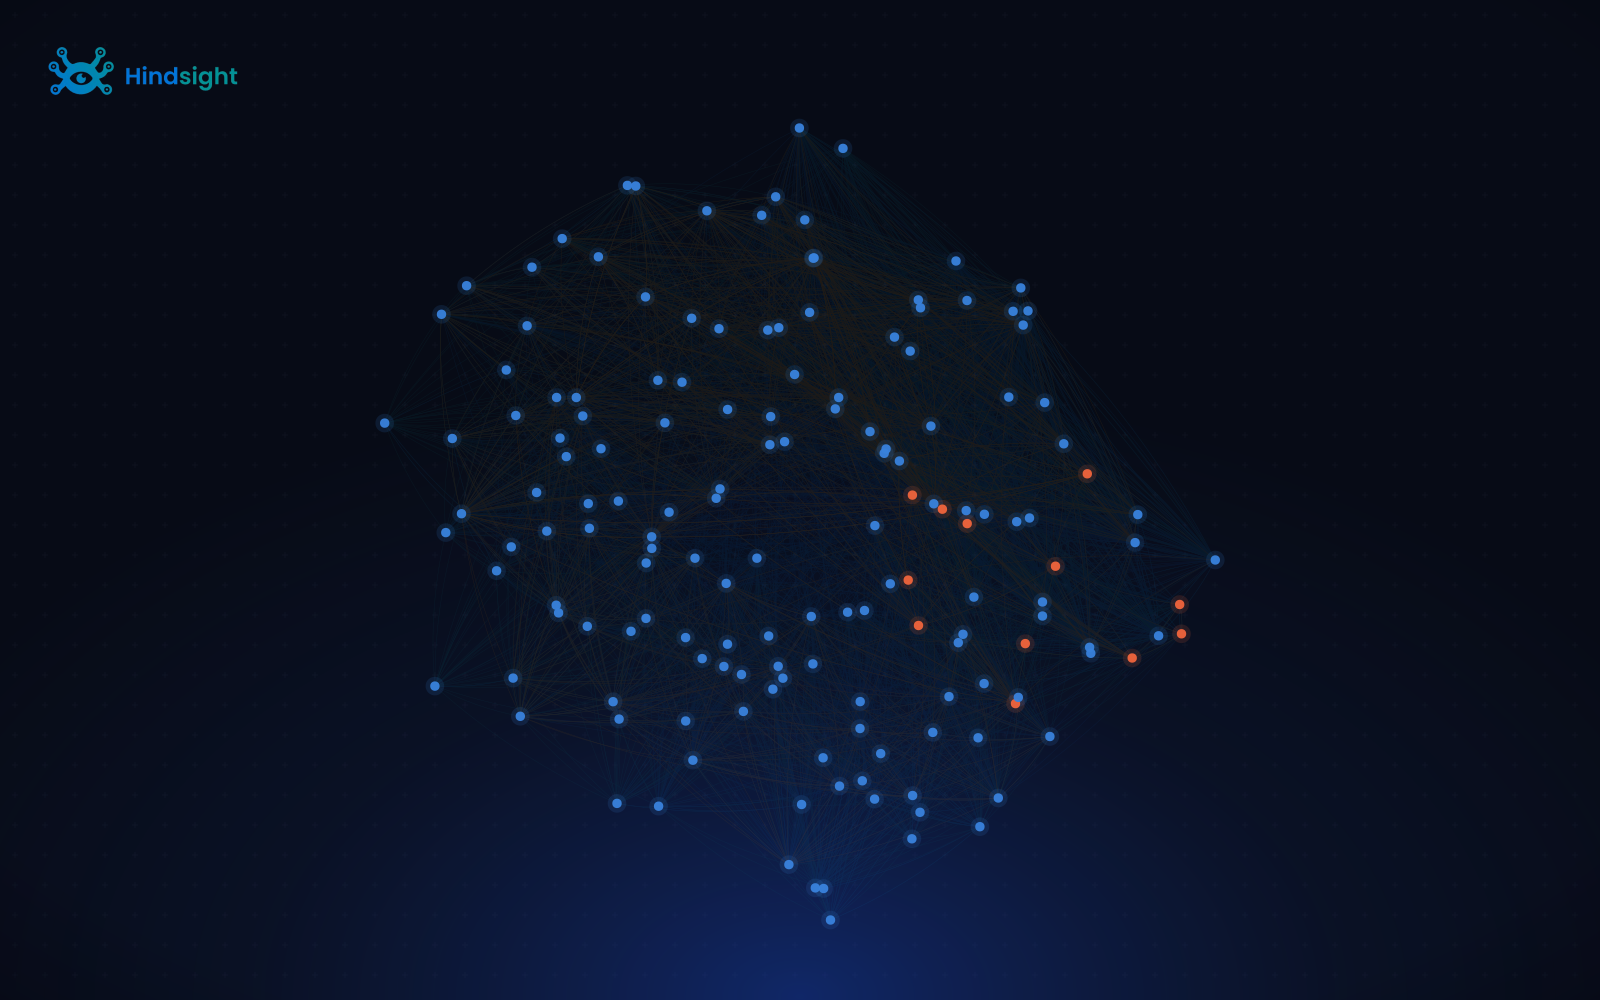
A dense constellation of glowing blue nodes connected by threads of light on a dark background, representing Hindsight's memory graph.

That's Hindsight's live memory graph — the “thought map” my chatbot actually consults before it answers a question about me. Fifteen-plus years of roles, projects, and hard-won lessons, wired together as context instead of flattened into a timeline.

Because this environment intentionally stores real credentials and configuration for easy rebuild and versioning, it's kept private — happy to walk through the architecture in an interview.

Resume

The short version: Principal DevSecOps/SRE engineer, 15+ years automating secure Kubernetes, GitOps, and Infrastructure-as-Code platforms across federal and enterprise environments. Active Top Secret clearance, Security+ certified. For the full work history, skills, and project details, see the complete resume.

Get in Touch

Open to new opportunities — feel free to reach out.